maybe your set of cipher suites is more restrictive than you were using with openssl s_client and the issue is that they don’t allow for whatever the remote is using?
I tried without that too
Just the prefer OpenSSL config
Just wanted to follow up and add to this:
KumoMTA internal: failed to connect to any candidate hosts: All failures are related to OpportunisticInsecure STARTTLS. Consider setting enable_tls=Disabled for this site. ResolvedAddress { name: "liquidlabs.email.", addr: 136.144.155.180 }:25: EHLO after OpportunisticInsecure STARTTLS handshake status: failed: received corrupt message of type InvalidContentType
This is another error we receive. Is InvalidContentType related to the email mime in any way? Surely not?
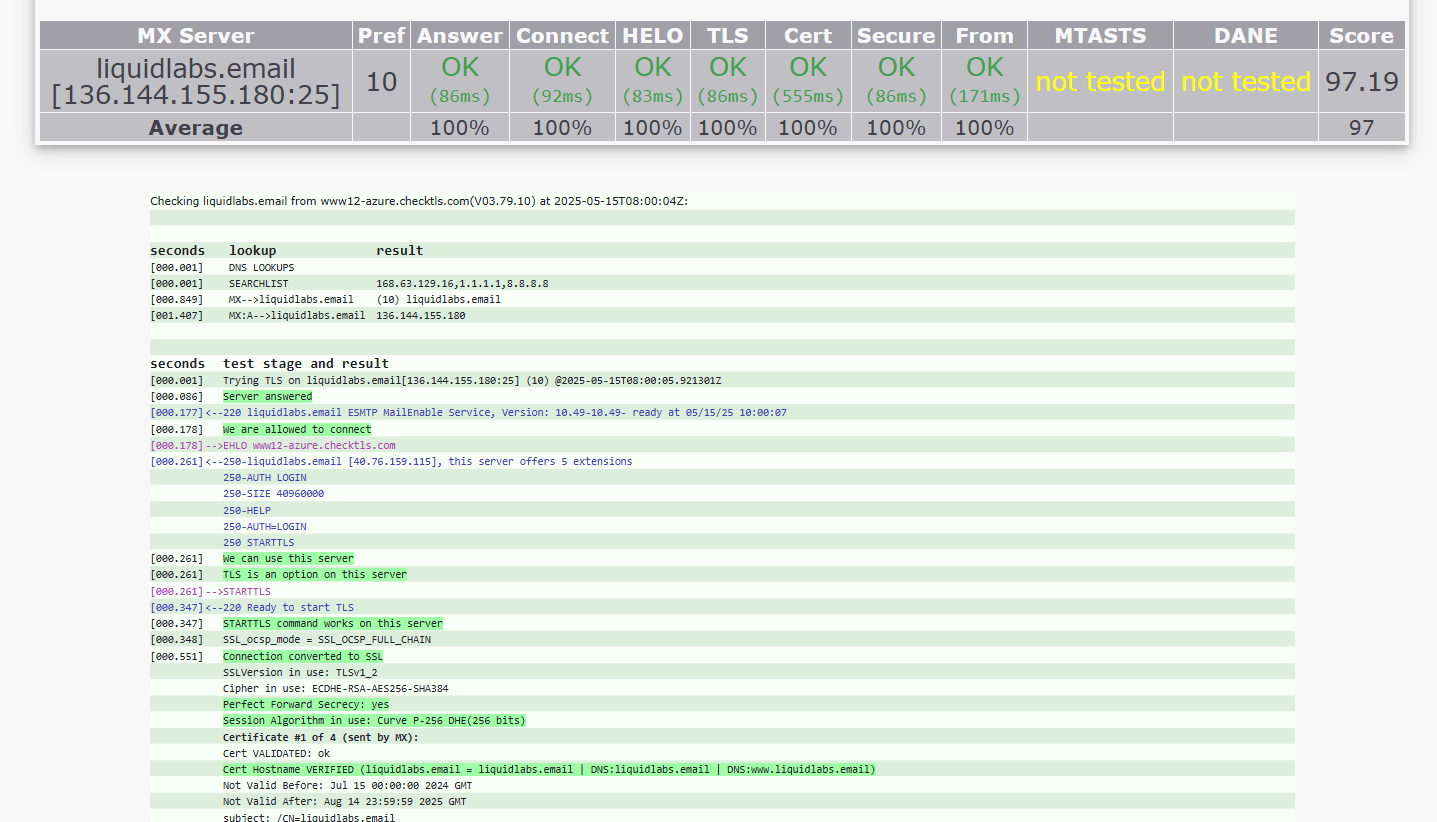
Target IP is different, which could be a factor
That seems the same, though. The IP from Kumo and CheckTLS matches